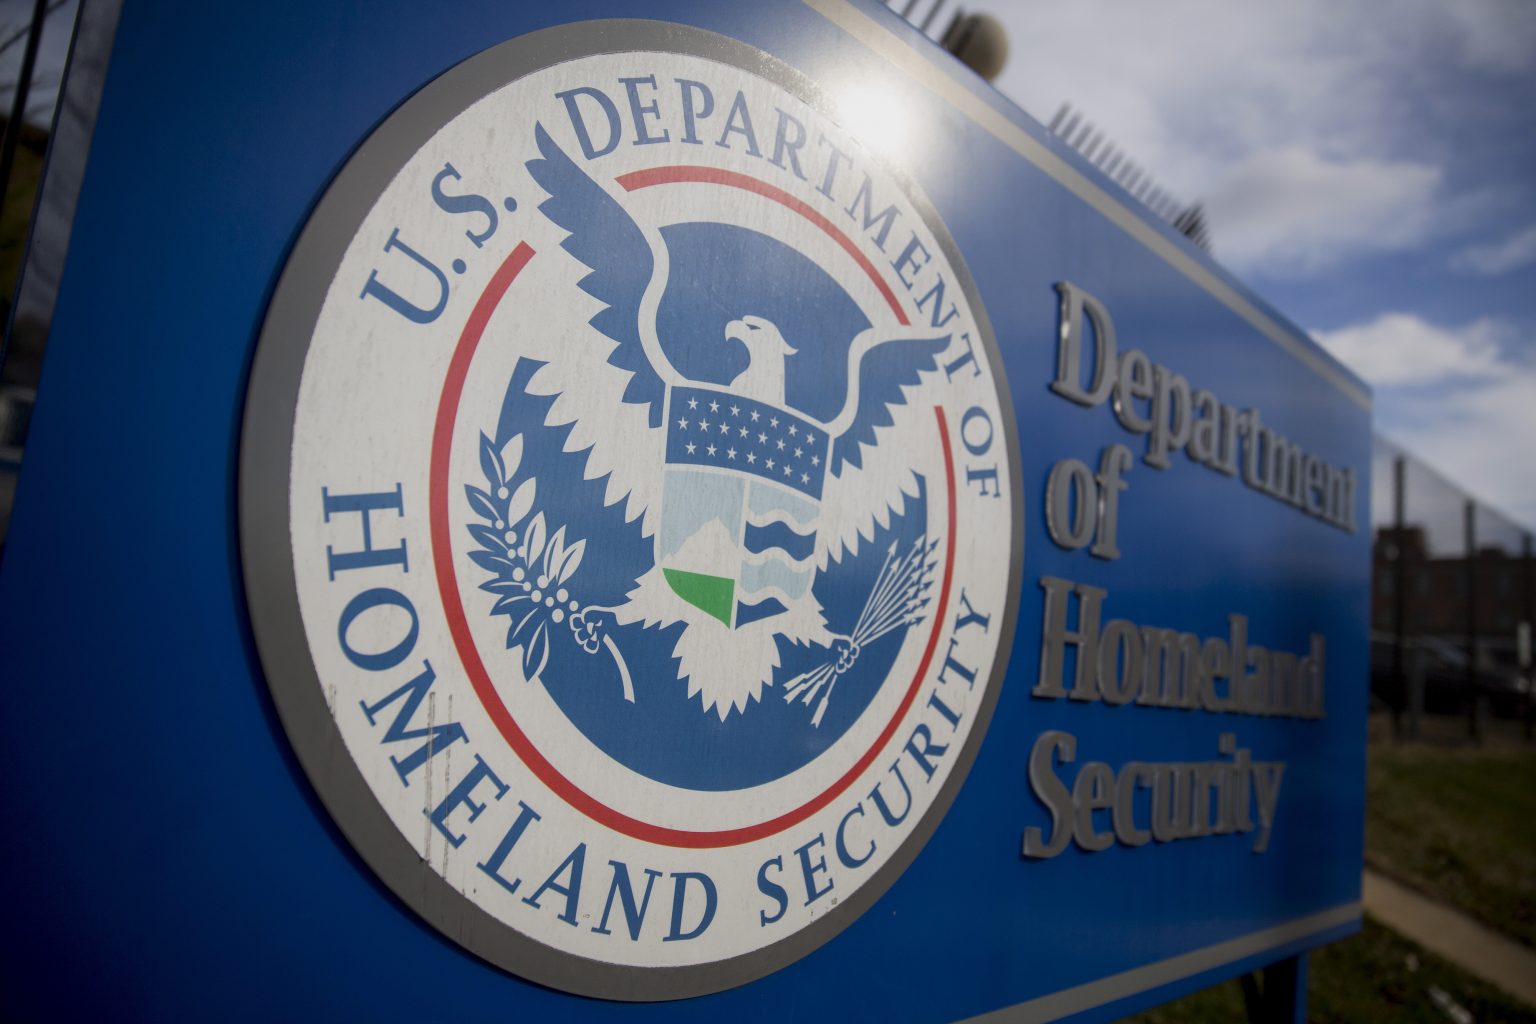
The Department of Homeland Security is investigating a major cybersecurity breach that exposed information on more than 40,000 federal employees and contractors, including Immigration and Customs Enforcement officers, Border Patrol agents and personnel involved in undercover operations. A hacking group calling itself the Department of Peace claimed responsibility for obtaining the records, which were subsequently published online in a searchable database. The leaked information reportedly includes employee names, government contact information, job titles, supervisors and internal access classifications, raising concerns about officer safety, compromised investigations and potential targeting by criminal organizations or political extremists. Federal officials are working to contain the exposure, while White House border czar Tom Homan has condemned the disclosure and confirmed a Justice Department investigation. The incident highlights serious vulnerabilities in federal information security at a time when immigration enforcement personnel face heightened political hostility and threats.
Key Takeaways
• More Than 40,000 Personnel Exposed: Leaked records identify federal immigration officers, contractors and potentially undercover personnel, creating security risks extending beyond ordinary employee contact information.
• Hackers Claim Political Motivation: The Department of Peace claims the disclosure was intended to expose immigration enforcement operations, while federal officials warn that publishing personnel information could facilitate harassment, intimidation and physical attacks.
• Federal Investigation Underway: DHS and the Justice Department are examining the incident as officials seek to contain the disclosure, protect affected personnel and determine how the information was obtained.
In-Depth
The Department of Homeland Security is investigating a potentially catastrophic cybersecurity breach after hackers exposed records identifying more than 41,000 federal employees and contractors, including thousands of immigration enforcement officers and undercover agents.
The compromised information reportedly includes approximately 10,000 Immigration and Customs Enforcement personnel and more than 20,000 Customs and Border Protection employees. Records contain names, employment locations, telephone numbers, email addresses and internal system classifications, potentially revealing sensitive operational relationships.
An anti-fascist hacking organization identifying itself as the Department of Peace claimed responsibility. The information was subsequently distributed through an online archive and searchable database, allowing users to identify individual officers and examine portions of the department’s organizational structure.
The disclosure raises significant national security concerns, particularly for undercover investigators whose identities could be exploited by criminal organizations. Exposed personnel also face potential harassment, intimidation and threats against their families.
White House border czar Tom Homan condemned the incident, confirming that the Justice Department is investigating. Federal officials have also sought removal of the information from internet hosting services, warning that its continued availability threatens employee safety.
The hackers reportedly obtained records associated with an identity-management system, although the technology provider denies evidence that its own systems were compromised. Investigators have not publicly established the precise intrusion method.
The incident underscores the vulnerability of federal personnel databases and the consequences of politically motivated cyberattacks. Protecting sensitive government information remains essential to preserving law enforcement effectiveness, safeguarding federal employees and preventing ideological disputes from becoming threats to public safety.