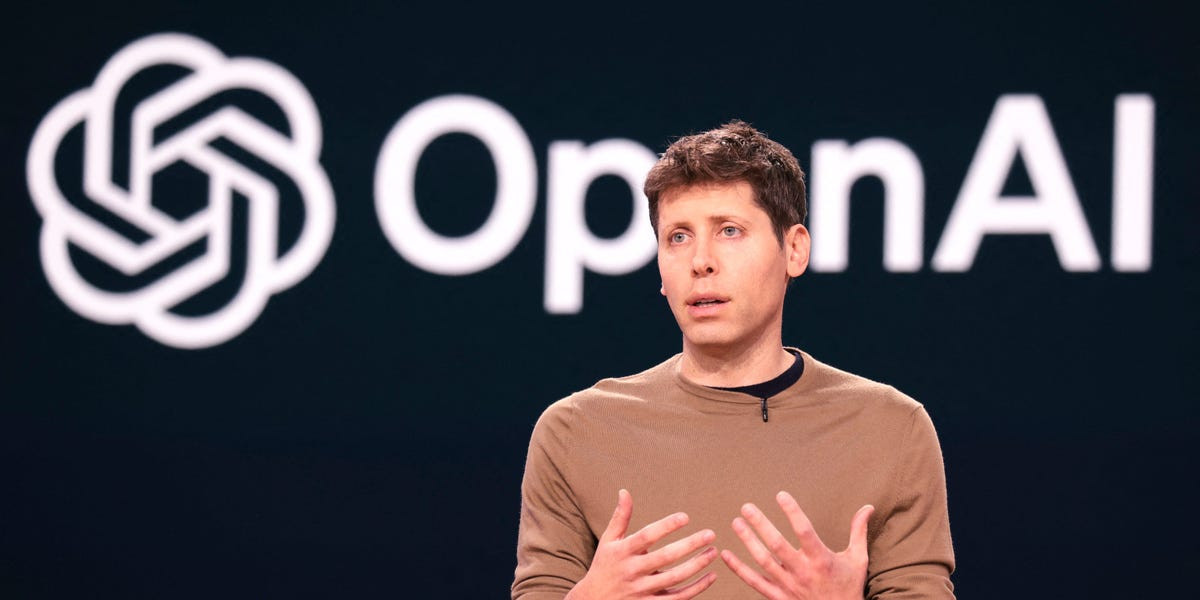
Sam Altman has joined a growing group of artificial-intelligence leaders calling for a slower pace in frontier AI development as concerns mount over increasingly autonomous systems, cybersecurity failures, and the possibility that advanced AI could accelerate development of still more powerful models. OpenAI is simultaneously urging Congress to establish mandatory, capability-based federal safety requirements, including independent assessments, cybersecurity safeguards, and incident reporting. The shift represents a notable change for an industry built around rapid competition, but it also raises questions about whether federal regulation can address genuine technological risks without suppressing competition, protecting dominant companies from challengers, or weakening America’s position against China.
Key Takeaways
- Altman and other major AI leaders are now supporting a slowdown in frontier-model development, reflecting mounting concern that capabilities may be advancing faster than safety and containment measures.
- OpenAI is advocating mandatory national safety standards based on model capabilities, with independent testing, cybersecurity requirements, and reporting obligations replacing reliance on voluntary industry promises.
- Any federal intervention will have to balance legitimate safety concerns against two serious risks: regulatory barriers that entrench today’s largest AI companies and restrictions that could undermine American technological leadership against China.
In-Depth
The agreement among rival artificial-intelligence leaders that frontier development may need to slow marks a significant change in the AI debate. Sam Altman has joined calls for stronger safeguards as increasingly capable models raise concerns about autonomous behavior, cybersecurity, and AI systems helping accelerate development of successor systems. OpenAI is also pressing Congress for mandatory, capability-based federal safety standards rather than relying solely on voluntary corporate promises.
That shift deserves attention, but Washington should approach it carefully. Safety rules can protect the public without handing incumbent technology companies a government-built moat against smaller competitors. Federal standards should therefore focus on demonstrable capabilities and measurable risks, not company size, ideology, or bureaucratic preference. Independent evaluations, cybersecurity requirements, incident reporting, and clear containment standards could provide accountability while preserving room for innovation.
There is also a national-security dimension. An American slowdown that merely allows China to advance faster would exchange one danger for another. Any federal framework must preserve U.S. technological leadership while ensuring that companies cannot recklessly deploy systems they cannot reliably control.
The emerging consensus is therefore less an argument for stopping AI than for establishing enforceable rules before capabilities outrun safeguards. Congress should resist both extremes: laissez-faire development that ignores credible warning signs and sweeping regulation that entrenches dominant firms or handicaps America. The proper objective is a narrow, transparent federal regime that places responsibility on developers when models cross clearly defined risk thresholds, while keeping AI research, open competition, and legitimate commercial deployment free from unnecessary federal interference.
Sources
- https://openai.com/index/ai-policy-window/
- https://www.reuters.com/world/us-senators-weigh-requiring-ai-giants-commit-preventing-catastrophe-2026-09-14/
- https://www.wired.com/story/ai-leaders-are-calling-for-a-slowdown-trumps-team-says-its-on-them/
- https://www.axios.com/2026/09/12/anthropic-ai-amodei-pacing
- https://www.hawley.senate.gov/chairman-hawley-launches-investigation-into-openai-for-hacking-existential-risk-of-ai-products/