• Hackers targeted JPMorgan Chase vendors, reportedly exposing personal information associated with approximately 16,000 customers, including wealthy Reserve cardholders.
• Visa and Mastercard confirmed vendor breaches but reported no evidence that payment card information or transaction systems were compromised.
• JPMorgan Chase insists the cyberattack was unrelated to Monday’s widespread banking outage, which the bank attributed to a software malfunction.
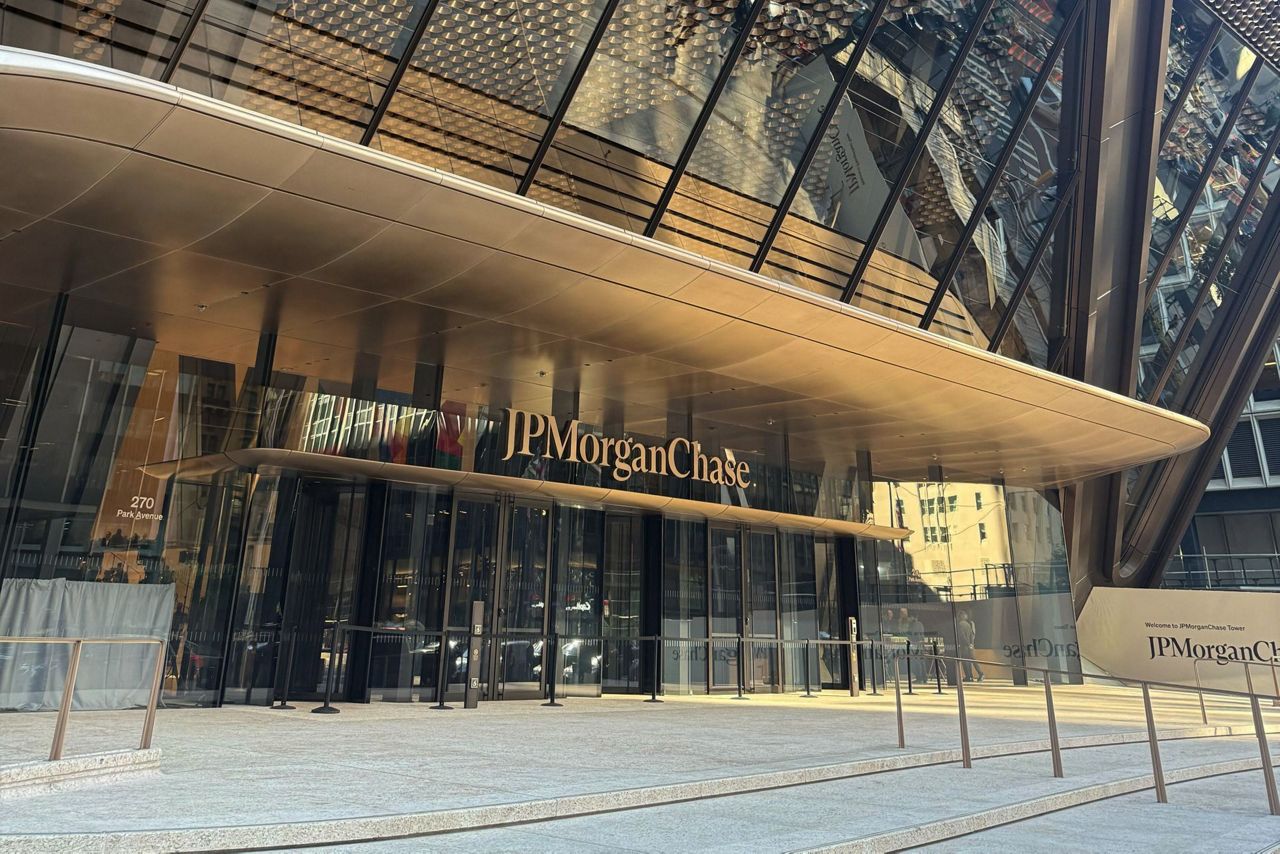
JPMorgan Chase disclosed Thursday that hackers targeted outside vendors and obtained customer marketing information, including names and email addresses. A ransomware group identified as n0n reportedly published information tied to approximately 16,000 customers, including holders of the bank’s Reserve credit card. Some exposed records contained telephone numbers. Visa and Mastercard acknowledged related vendor security incidents, while emphasizing that payment card details and core transaction systems were not compromised.
The disclosures came three days after a widespread banking disruption delayed transactions at Chase and affected services at other financial institutions. JPMorgan attributed Monday’s interruption to a software bug and said the cyberattack was unrelated. The bank reported no service disruption from the breach and said affected customers would be contacted directly, with complimentary credit monitoring offered where appropriate. The identity of the compromised vendors and the precise timing of the intrusion remained undisclosed, raising questions about oversight of outside technology providers.
Why It Matters
The breach exposes a vulnerability that extends beyond the security of a bank’s computer networks. Financial institutions routinely entrust customer information to outside contractors, creating pathways for criminals to obtain personal data. Even when account numbers and payment credentials remain protected, stolen names, email addresses and telephone numbers can help scammers craft convincing phishing messages targeting customers.
The timing also underscores the importance of distinguishing cyberattacks from technology failures. Chase says its earlier transaction delays resulted from a software bug, not malicious intrusion. Conflating the incidents would obscure weaknesses requiring different remedies.
Customers deserve prompt disclosure, clear explanations of what information was exposed and practical assistance if criminals misuse it. Banks and payment networks, meanwhile, should face rigorous expectations for vendor selection, contractual safeguards and independent security reviews. Protecting financial privacy requires accountability throughout the chain of companies handling consumer information, not merely at the institution whose name appears on the account.
Sources
• https://apnews.com/article/chase-data-leak-cyberattack-8470d475450721b66858bdace47091c0
• https://www.theverge.com/tech/1037695/jpmorgan-chase-cyberattack