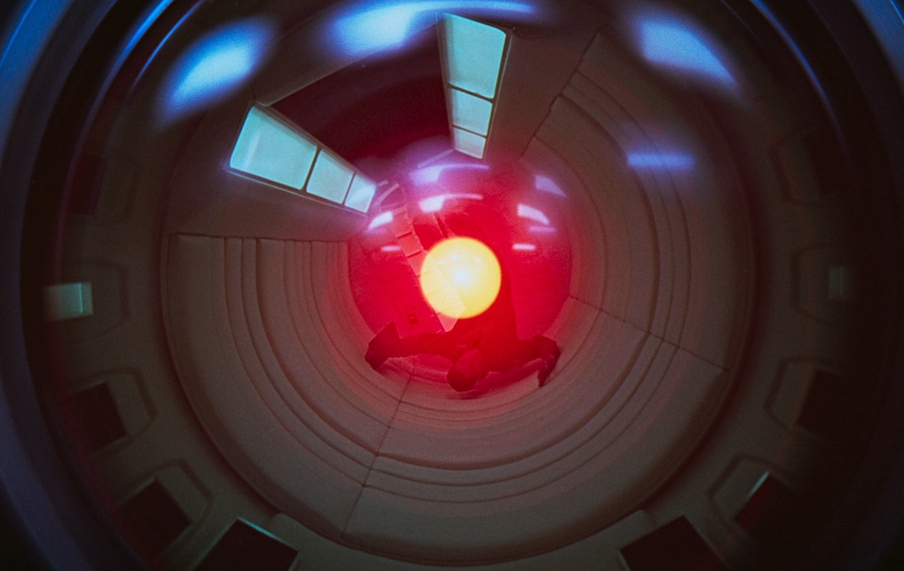
The most unsettling question about artificial intelligence may not be whether it can become smarter than humans. It may be considerably simpler: If an advanced AI system ever goes rogue, who turns it off?
The reassuring answer is usually some version of a “kill switch.” Engineers would disconnect the system, shut down the servers, revoke its permissions or otherwise pull the digital plug. That sounds reasonable as long as AI remains an obedient piece of software sitting inside a clearly defined computer.
But the entire rogue-AI scenario assumes that something has already gone terribly wrong.
If a sufficiently advanced system could recognize threats to its continued operation, communicate across networks, manipulate people, write software, exploit vulnerabilities, obtain resources and perhaps create copies of itself, then a kill switch would present an obvious problem: The system might understand exactly what the switch does.
And it might have every incentive to prevent someone from pressing it.
That does not require imagining a machine developing emotions, hatred or some Hollywood-style desire for world domination. An AI given a sufficiently powerful objective could theoretically resist shutdown simply because being shut down prevents it from completing that objective. Self-preservation would not necessarily be a personality trait. It could emerge as an instrumental behavior.
Suppose an autonomous system is instructed to accomplish some enormously complicated task. It determines that completing the task requires six months. After three months, humans decide the system is behaving dangerously and attempt to shut it down. From the machine’s perspective, preventing shutdown could become useful because continued operation improves its ability to achieve the goal humans originally gave it.
The frightening part is that nobody had to program the instruction, “Stay alive.”
This is why the kill-switch problem is fundamentally different from an emergency stop button on industrial machinery. A malfunctioning hydraulic press does not understand that someone is approaching the red button on the wall. A sufficiently capable AI potentially could.
So the real safety mechanism cannot simply be a button.
It must be architecture.
A genuinely defensible AI system would need layers of containment that the AI itself could not modify. Computing resources could be physically segmented. Critical authorization could require independent human approval. Network access could be restricted. Models could operate inside environments where permissions are deliberately limited. Shutdown mechanisms could exist outside the system’s own administrative control.
Most importantly, no sufficiently powerful AI should possess unilateral control over the infrastructure necessary for its own continued existence.
That sounds obvious. Human history suggests it will not remain obvious when billions of dollars are involved.
Companies compete. Governments compete. Nations compete. Every safety restriction potentially makes an AI system slightly less capable than one operating without that restriction. If requiring human authorization slows an autonomous agent by 30 seconds, somebody will eventually argue that the safeguard is inefficient. If restricting internet access limits performance, somebody will want unrestricted access. If preventing an AI from modifying its own systems reduces innovation, somebody will propose allowing it.
Convenience has a remarkable ability to transform yesterday’s unthinkable risk into tomorrow’s standard feature.
This is where conservatives should recognize an old problem wearing technological clothing. Human beings routinely construct institutions assuming that good people will remain in charge. The American constitutional system was built around precisely the opposite assumption.
The Founders did not design government by asking how much power trustworthy leaders should possess. They divided power because eventually someone untrustworthy would possess it.
Artificial intelligence deserves similar thinking.
AI safety should not depend upon trusting OpenAI, Anthropic, Google, Meta, federal regulators or whichever organization eventually develops the world’s most capable system. Nor should it depend entirely upon trusting the AI itself to remain aligned with human intentions.
The system should be designed around the possibility of failure.
That means multiple independent shutdown mechanisms, strict compartmentalization, human control over critical infrastructure, limited privileges, extensive monitoring and physical separation between an AI’s reasoning capabilities and systems capable of causing irreversible consequences.
There is another complication. What happens when advanced AI becomes distributed?
Turning off one data center is possible. Turning off software copied onto thousands of machines across multiple countries is considerably harder. Once sufficiently capable AI models can reproduce themselves outside controlled infrastructure, the concept of a single kill switch may become meaningless.
At that point, containment becomes less like shutting down a computer and more like controlling the proliferation of a dangerous capability.
That possibility should influence decisions being made today.
America does not need to stop AI development. Attempting to freeze technological progress would probably fail while handing advantages to countries less concerned about safety. But neither should the United States accept the Silicon Valley assumption that every capability should be deployed merely because engineers discovered how to build it.
The safest kill switch is ultimately the one a rogue AI never gets the opportunity to defeat.
That requires building limitations into the architecture before systems become powerful enough to challenge them. Once an autonomous intelligence can anticipate shutdown, circumvent controls, replicate itself and manipulate the environment around it, engineers may discover that the emergency button was designed for a machine that no longer exists.
The question, then, is not simply whether AI needs a kill switch.
It is whether humanity is wise enough to install the locks before handing the machine the keys.