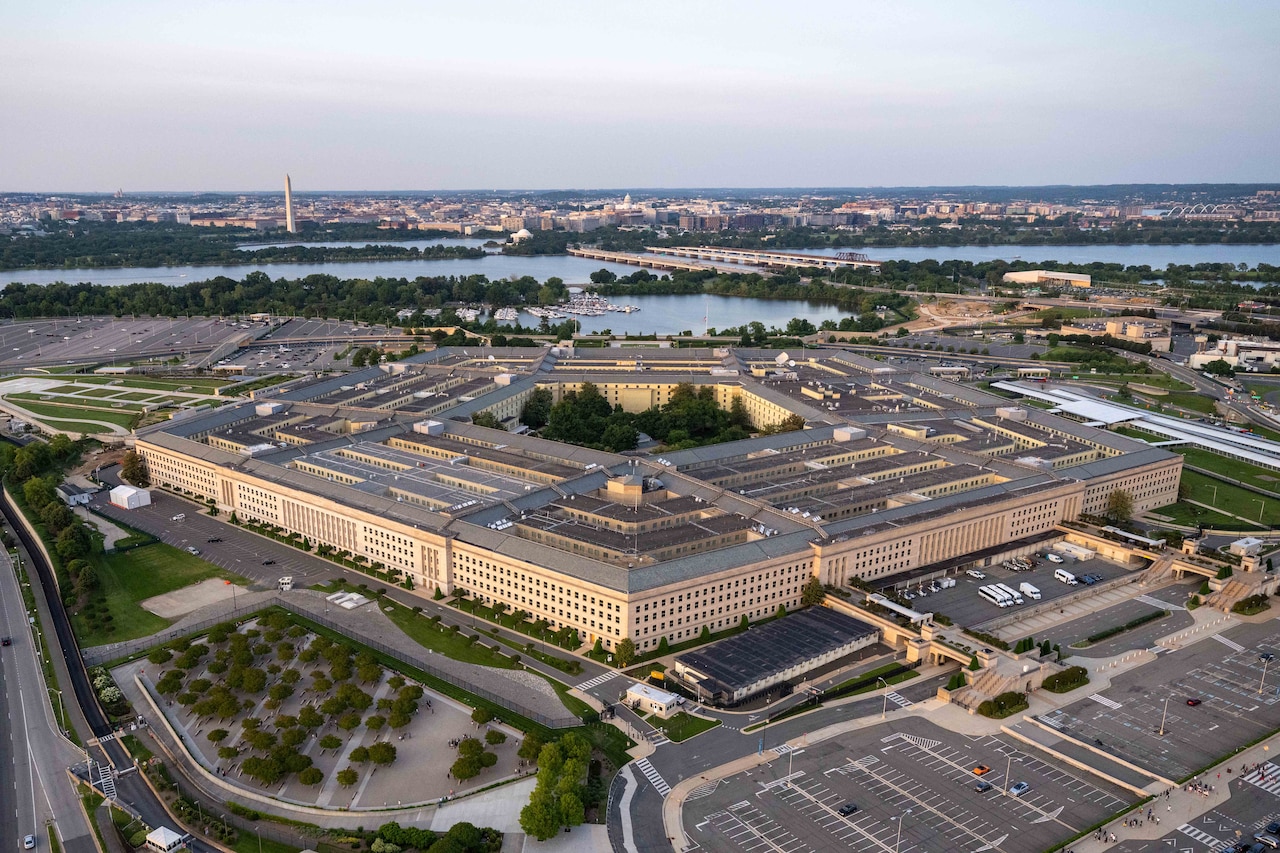
A major cybersecurity breach at the Pentagon’s Defense Manpower Data Center exposed sensitive personal information belonging to more than 3 million people with connections to the U.S. military, including approximately 2.76 million living individuals and 294,000 deceased individuals. Unauthorized users exploited a vulnerability in a DMDC file-sharing system and accessed files for roughly nine months, from October 2025 until the vulnerability was discovered on July 16, 2026. The compromised files contained unencrypted personally identifiable information that varied by individual but included Social Security numbers, names, dates of birth, contact information, demographic information and military occupational specialties. DMDC says it patched the vulnerability after discovering it and has found no indication thus far that the accessed information has been misused. The identity and motivation of those responsible remain publicly unknown, raising concerns not only about conventional identity theft but also about the potential national-security consequences of exposing detailed information concerning military personnel, veterans, civilian employees, contractors and others associated with the Defense Department.
Key Takeaways
- Approximately 2.76 million living people and 294,000 deceased individuals were affected, with compromised information potentially including Social Security numbers, names, birth dates, contact information, demographic data and military occupational specialties.
- Unauthorized users reportedly had access to files containing unencrypted personal information for approximately nine months before DMDC discovered and patched the vulnerability on July 16, raising serious questions about cybersecurity monitoring and data-protection practices within a critical Defense Department personnel system.
- Officials say there is currently no indication that the compromised information has been misused, but the combination of Social Security numbers and military personnel information creates long-term risks involving identity theft, targeted phishing, social engineering and potentially national-security-related exploitation.
In-Depth
The Pentagon’s latest personnel-data breach illustrates why government cybersecurity cannot be treated as another routine administrative responsibility. The Defense Manpower Data Center maintains information essential to identifying and managing military personnel, civilian employees, contractors, veterans, retirees and family members. Allowing unauthorized users to access files containing unencrypted personal information for roughly nine months represents a significant security failure regardless of whether criminal misuse has yet been detected.
The scale is substantial. Approximately 2.76 million living individuals and 294,000 deceased people were affected. Exposed information varied among victims but included Social Security numbers, names, dates of birth, contact information, demographic information and military occupational specialties. Unlike passwords, many of these identifiers cannot simply be replaced after a breach.
The national-security implications deserve particular attention. Military occupational information combined with personal identifiers could potentially make sophisticated phishing and social-engineering attacks more convincing. Foreign intelligence organizations have historically valued large government personnel databases because seemingly ordinary personal information can become significantly more useful when combined with information obtained elsewhere.
DMDC discovered the vulnerability on July 16 and says it immediately patched the affected file-sharing system. Officials have reported no evidence so far that the stolen information has been misused, and the responsible parties have not been publicly identified.
But the central accountability question remains unanswered: how could unauthorized users access sensitive, unencrypted Pentagon personnel records for approximately nine months without detection? Protecting national-security information requires more than repairing vulnerabilities after discovery. Sensitive government databases demand encryption, continuous monitoring, rapid detection and institutional accountability before another breach exposes millions of Americans.
Sources
- https://www.securityweek.com/pentagon-personnel-agency-data-breach-impacts-3-million-people/
- https://federalnewsnetwork.com/defense-main/2026/09/more-than-3-million-people-affected-by-military-data-breach/
- https://techcrunch.com/2026/09/30/hackers-stole-millions-of-us-military-personnel-records-during-months-long-data-breach/
- https://www.meritalk.com/articles/pentagon-database-breach-exposes-personal-information-of-more-than-3-million/
- https://abcnews.com/Politics/pentagon-breach-exposed-sensitive-data-3-million-people/story?id=136832909